Autonomous DAST + Human-led PTaaS
Continuous Penetration Testing. Zero False Positives. Built for Fast-Shipping Teams.
Find and fix exploitable vulnerabilities across your Web Apps, REST/GraphQL APIs, Cloud Perimeters, and AI Endpoints before attackers do. Combine automated CI/CD scanning with CREST-certified human pentesting for 100% audit-ready compliance.
5-minute setup • Safe, non-destructive production scanning • SOC 2, ISO 27001 & HIPAA ready
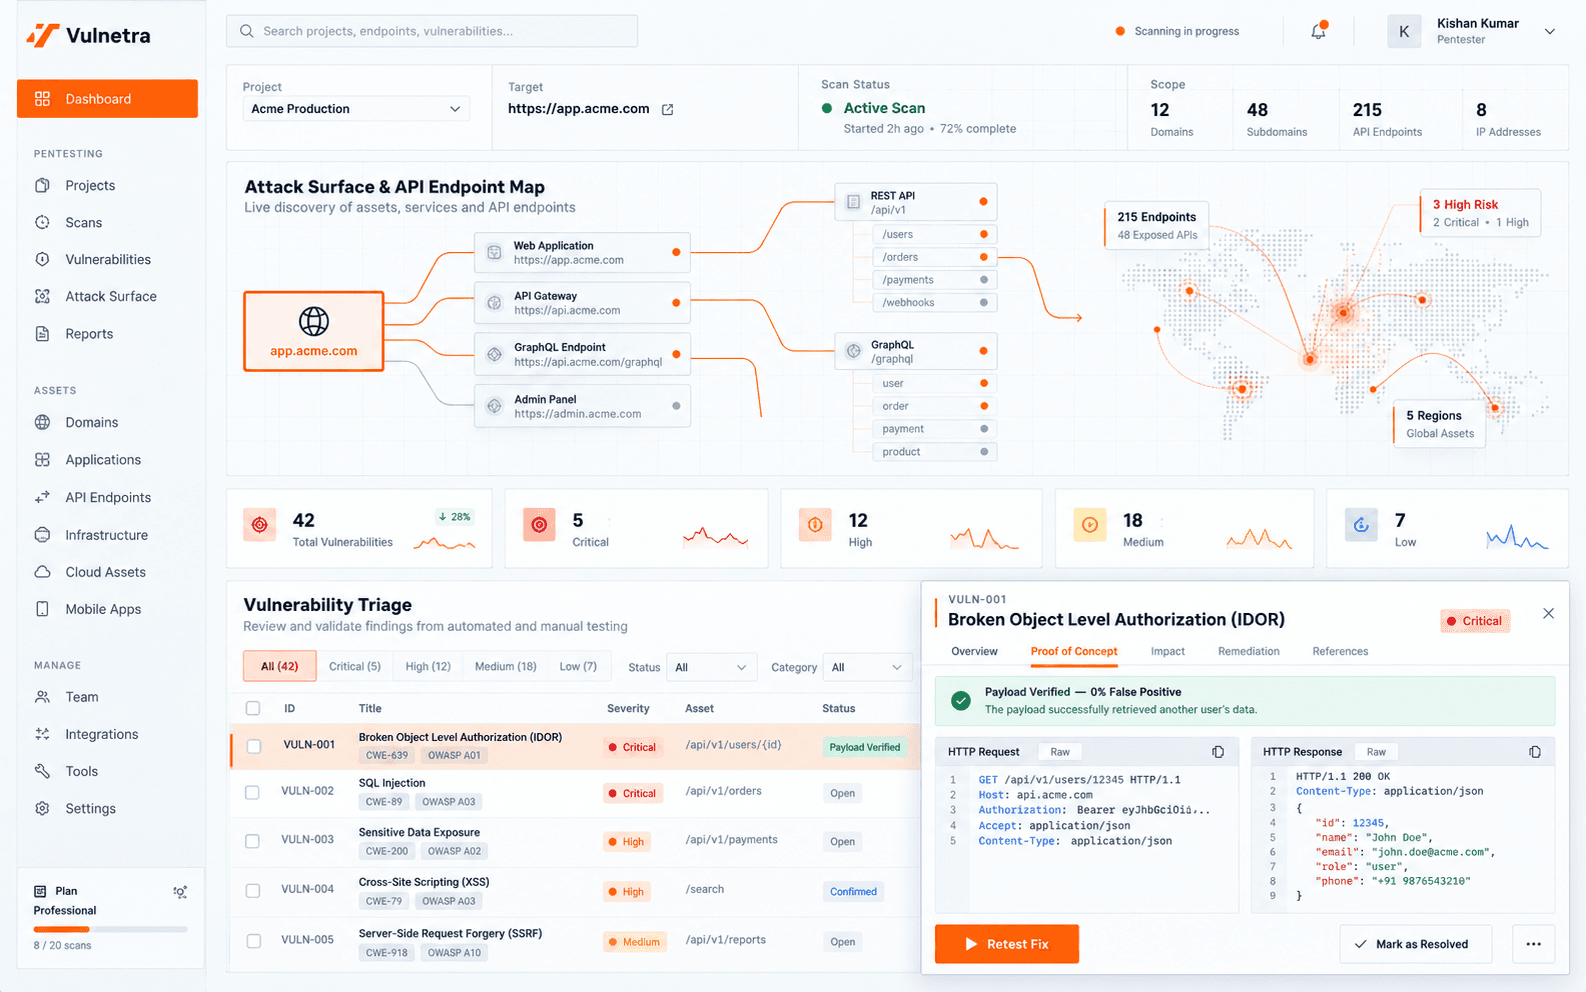
Live triage — IDOR payload-verified, 0% false positives
- 15,000+
- Active Offensive Vulnerability & CVE Checks
- 99.8%
- Payload-Verified True Positive Accuracy
- < 72 Hrs
- First Auditor-Signed Compliance Report
- 100%
- Audit Acceptance Guarantee (SOC 2 & ISO 27001)
Trusted by security-first engineering teams & approved by leading auditors
- SOC 2 Type II
- ISO 27001
- HIPAA
- PCI-DSS
- CREST
Stop choosing between slow $20,000 PDFs and noisy vulnerability scanners.
Modern engineering teams deploy code dozens of times a week. Point-in-time annual consultancies can't keep up, and legacy scanners drown your developers in false alerts.
 01
Obsolete & Slow
Point-in-Time Static PDFs
- Takes 4 to 6 weeks just to scope, schedule, and contract.
- Costs $15,000–$30,000 per single application assessment.
- Static 200-page PDF, outdated on next deploy.
- Zero integration with GitHub, Jira, or dev workflows.
 02
High Noise / Low Depth
Thousands of Unverified Alerts
- Floods backlogs with unverified CVE banner guesses.
- Blind to IDOR, business logic, privilege escalation.
- Breaks on React/Vue SPAs, GraphQL, MFA logins.
- Rejected by strict SOC 2 and procurement auditors.
 03
Continuous + Human-Vetted
Automated Speed + Human Offensive Depth
- Deploy in 5 minutes across Web, API, Cloud.
- 100% payload-verified proof, zero triage fatigue.
- Certified testers find logic, payment, AI flaws.
- 1-click retesting from Jira, Linear, GitHub, Slack.
Built to break modern architectures — before real attackers do.
Go far beyond surface-level port scanning. Our engine combines headless browser execution, schema-driven API fuzzing, and manual offensive research.
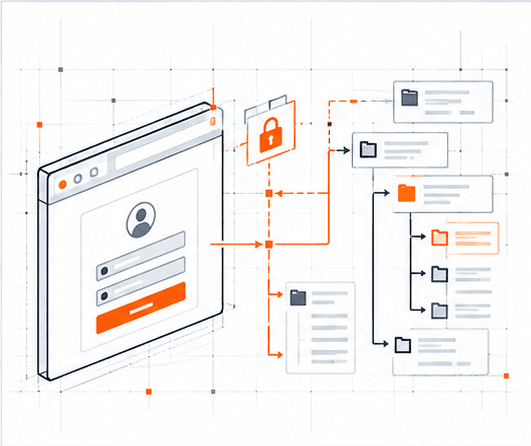
Authenticated DAST
Deep Web App & SPA Crawling
Navigate React, Next.js, Vue, Angular behind OAuth, SAML SSO, JWT, TOTP MFA. Maintains session state across multi-step journeys.
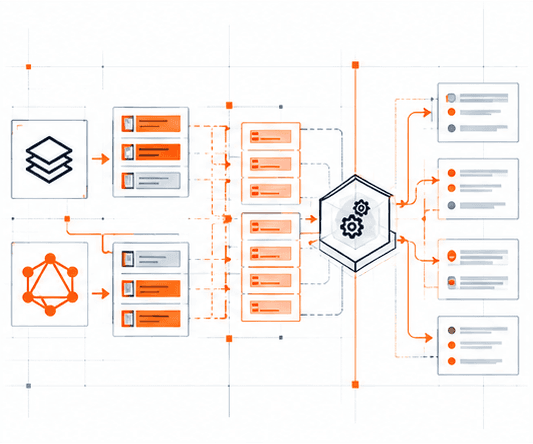
API Security
REST, SOAP & GraphQL Pentesting
Import OpenAPI or Postman in one click. Fuzz for BOLA/IDOR, mass assignment, rate-limit bypass, hidden params.
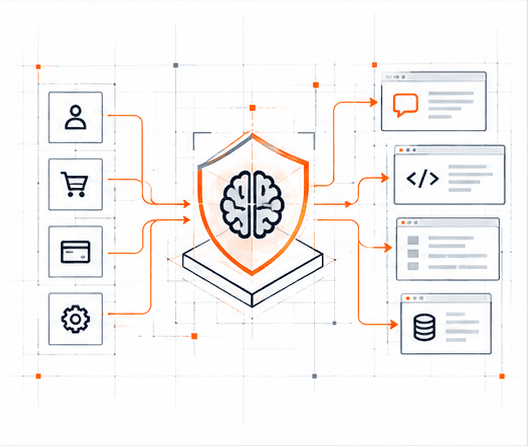
Offensive Research
Human-Led Business Logic & AI Testing
OSCP/CREST testers probe checkout manipulation, multi-tenant leaks, LLM prompt injection by hand.
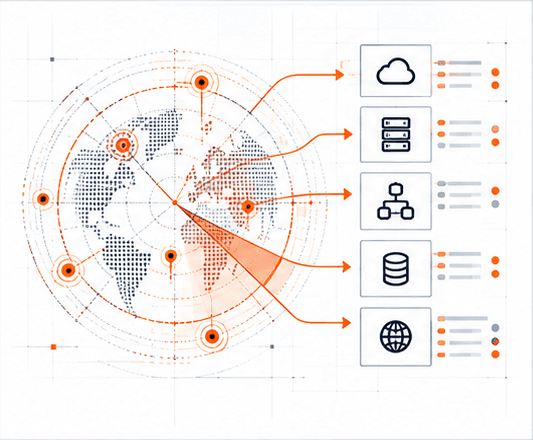
Perimeter Monitoring
Continuous Attack Surface Discovery
Map shadow subdomains, staging envs, open ports, AWS/GCP/Azure misconfigs before attackers do.
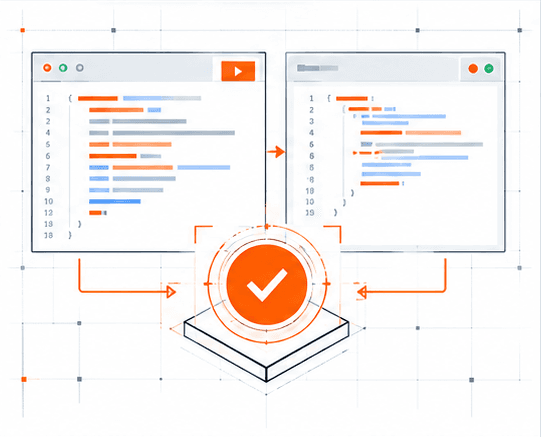
Zero-Noise Triage
Payload-Verified Zero False Positives
Every finding ships with exploit proof, HTTP logs, cURL replay, and video PoCs. No ghosts.
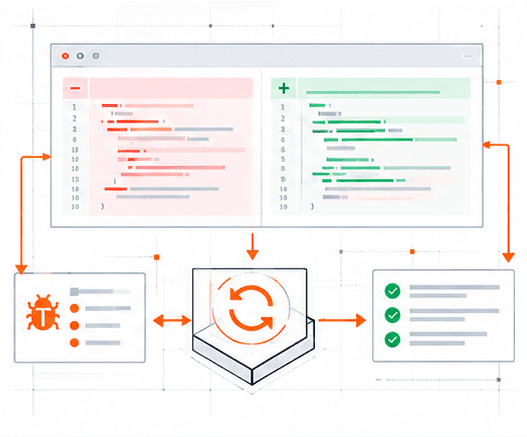
DevSecOps Velocity
Developer-Native Remediation & Retest
Push to Jira, Linear, GitHub with fix snippets. 1-click re-scan validates the patch in seconds.
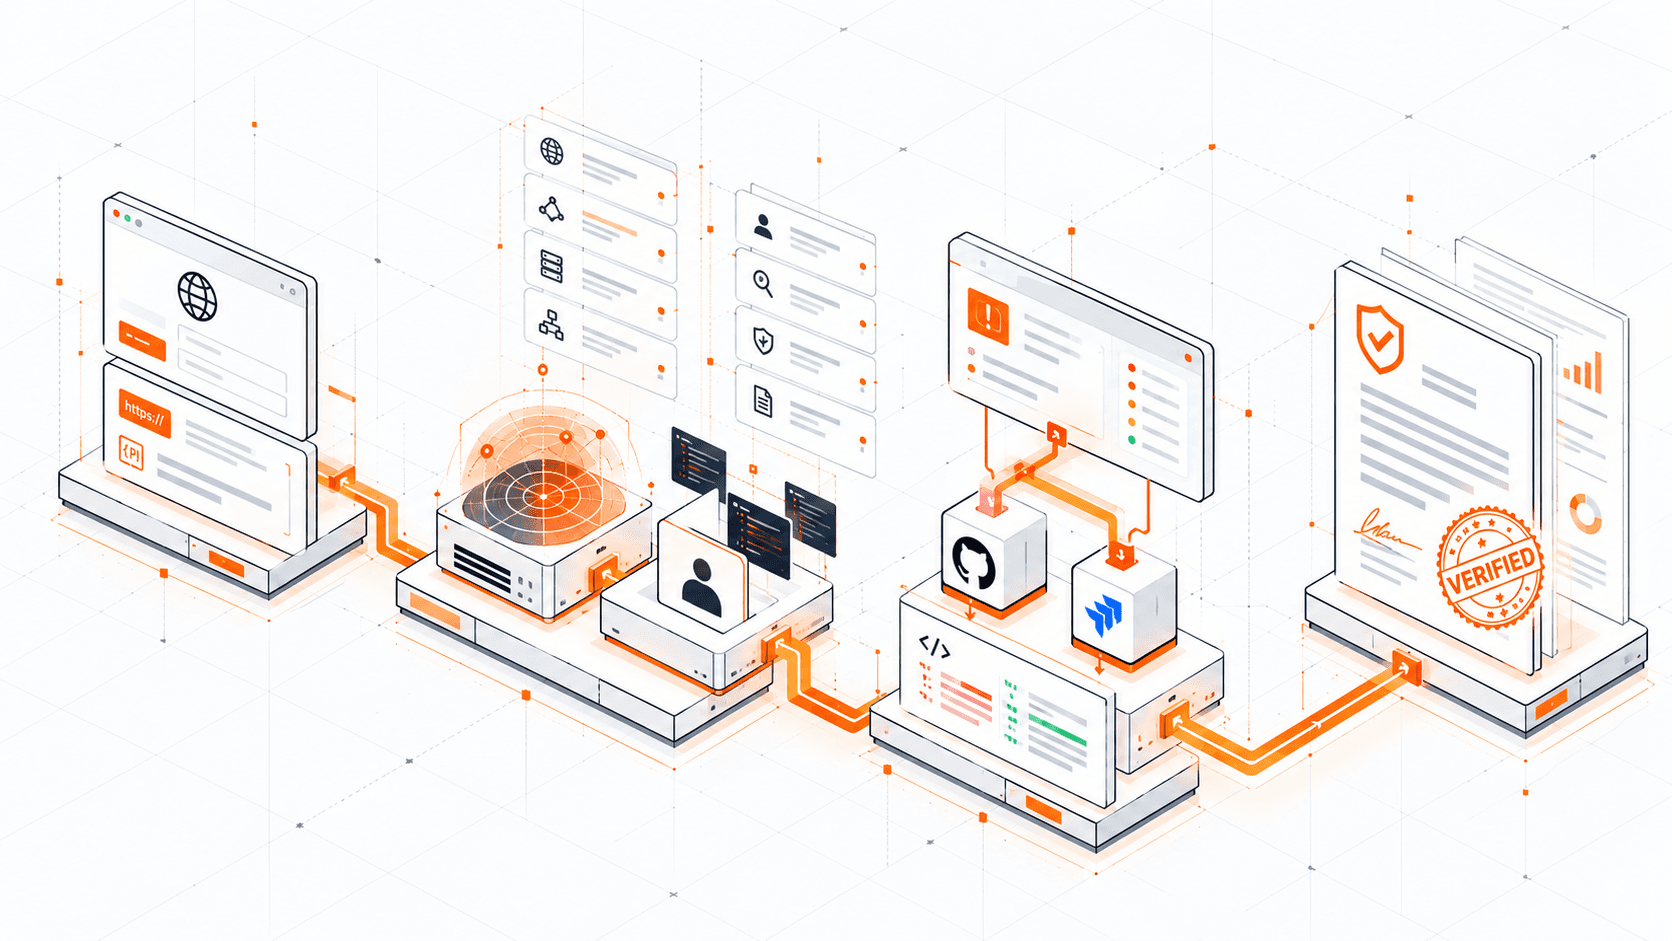
Continuous offensive security in four frictionless steps.
Step 01
Verify targets without heavy agents.
Add URLs, upload OpenAPI/Postman schemas, or connect AWS/GCP/Azure via read-only role. Set scan windows, RPS limits, login macros in minutes.
Output: Verified Attack Surface Inventory
Pass SOC 2, ISO 27001, and enterprise reviews on the first try.
Stop hiring a pentest agency two weeks before audit close. Every check maps to compliance controls — and syncs automatically with Vanta, Drata, Secureframe.
- SOC 2 Type I & II
- ISO/IEC 27001
- HIPAA
- PCI-DSS 4.0
- GDPR
- OWASP Top 10 & API 10
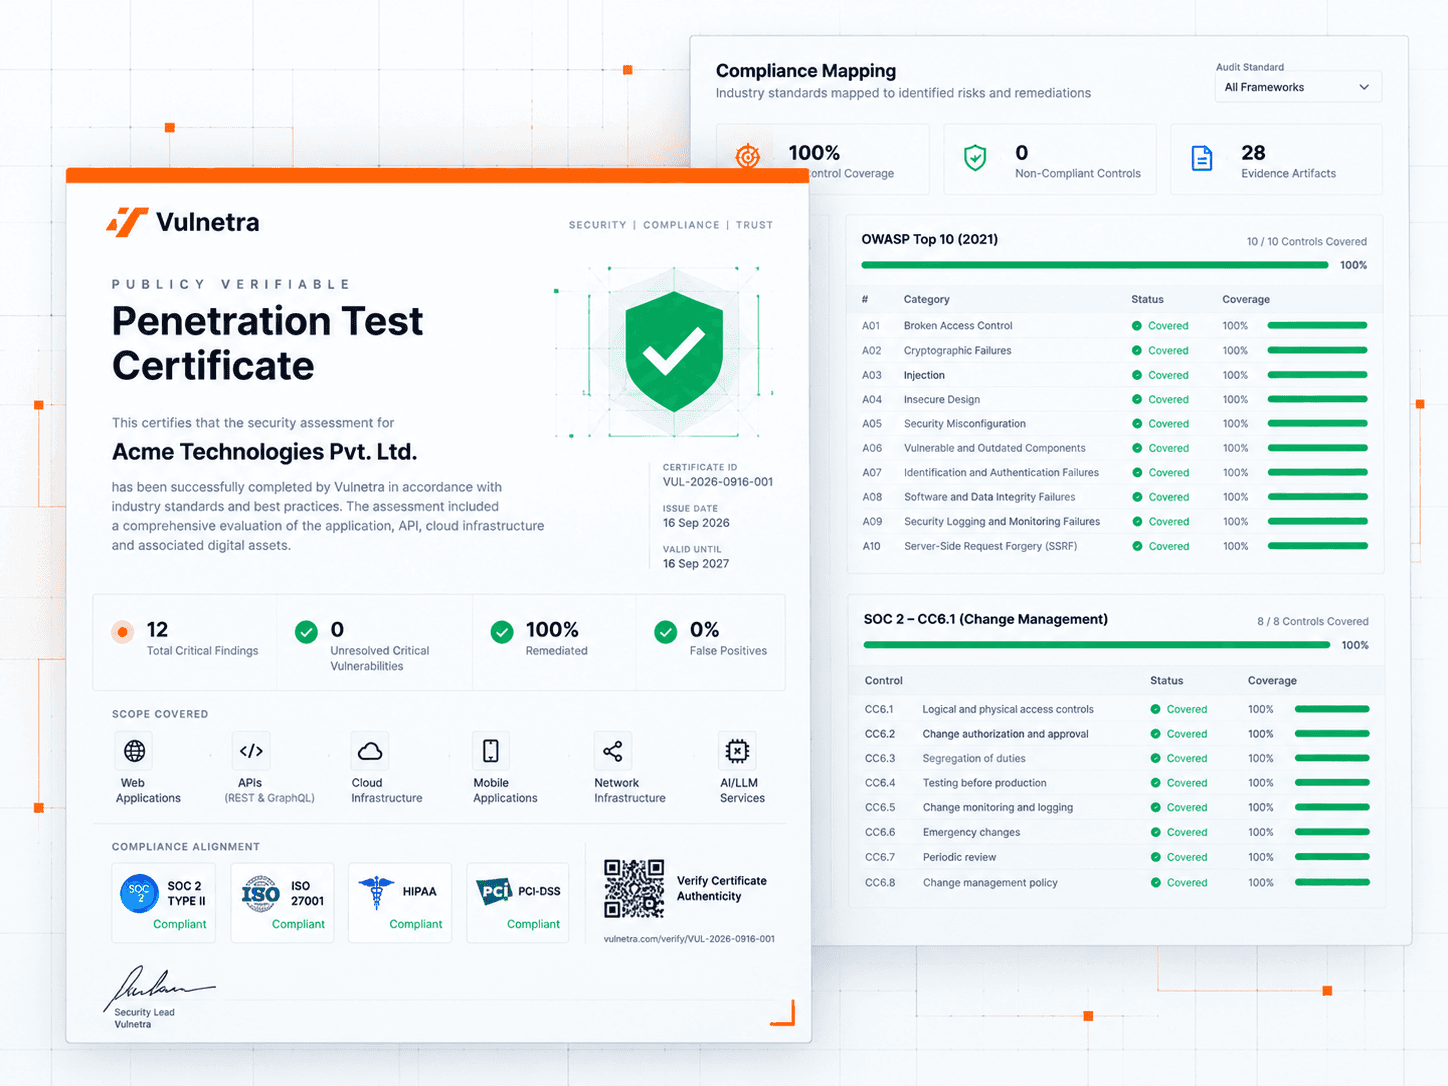
Publicly Verifiable Pentest Certificate
Turn security into a sales closer. Embed a verifiable badge on your site or Trust Center so procurement verifies scope and remediation instantly.
Security that lives where developers work.
No portal fatigue. Trigger scans on PRs, route bugs to trackers, sync evidence without spreadsheets.
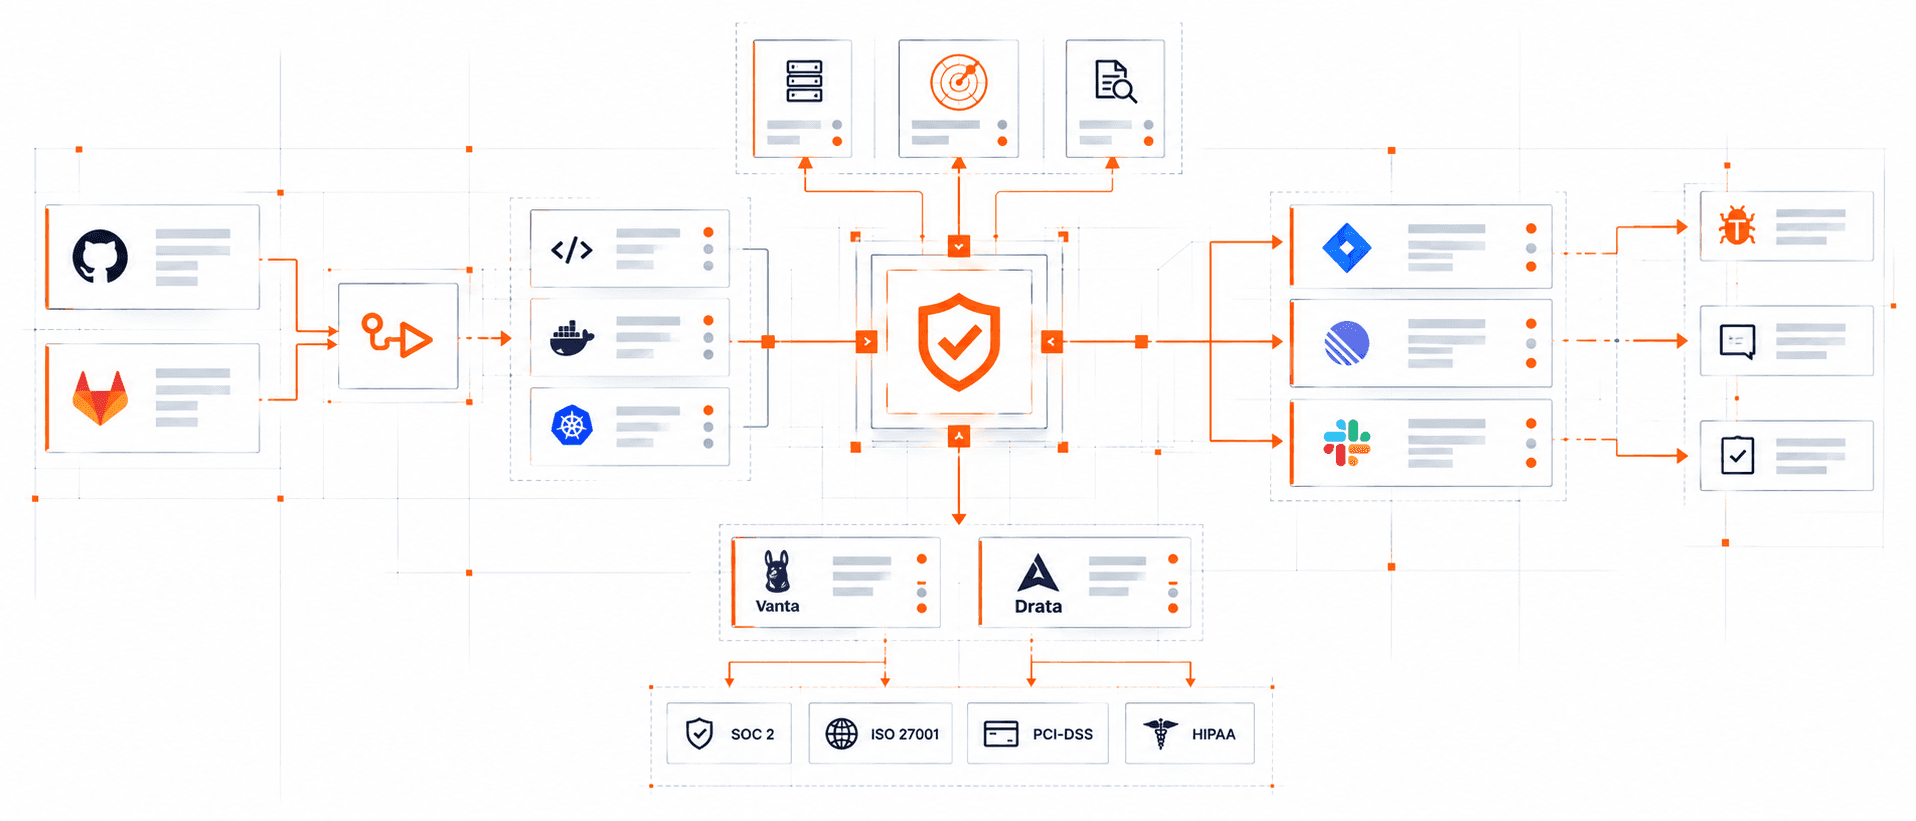
- GitHub Actions
- GitLab CI/CD
- Bitbucket Pipelines
- Jira Software
- Linear
- Slack
- Microsoft Teams
- Postman
- Vanta
- Drata
01
CI/CD Deployment Gates
Trigger targeted DAST and API scans on staging or prod when a release PR merges.
02
Bi-Directional Ticket Sync
Push to Jira, Linear, GitHub Issues; auto re-scan when devs mark tickets resolved.
03
Zero-Touch GRC Evidence
Push scan logs and signed reports directly into Vanta and Drata.
Why modern CTOs and AppSec leads switch.
78% Faster
Lower Mean Time to Remediate
“Legacy scanners flooded Jira with unverified alerts devs ignored. Payload-verified proof and video PoCs get fixed the same day.”
$18,500 Saved
Annually vs. Manual Consultancies
“We paid $22,000 yearly for a static PDF for SOC 2. Now continuous scanning plus two human pentests costs less than a third.”
3x Faster
Enterprise Questionnaire Sign-Off
“Sharing our live certificate and CREST-aligned report upfront killed security-review delays in our Q3 pipeline.”
Frequently Asked Questions
Complex microservices, multi-cloud, or AI app? Talk with an offensive engineer — not a scripted SDR.
Custom architecture review
Book a Technical Q&A Call →
Deploy in under 5 minutes
Ready to see what hackers see across your attack surface?
Start a 14-day free trial of automated DAST & API scanning, or book 15 minutes with an offensive architect to scope your compliance pentest.
No credit card required • Unlimited team seats • 100% Audit Acceptance Guarantee